

LOCAL VAULTS FOR HUMANS & AI AGENTS
No secrets in theprompt
The local secrets manager for humans and AI agents. Free vault. $0 forever. No cloud. No account. No subscription. Inject secrets into anything you run: terraform apply, docker compose up, npm run dev, pytest, cargo test, curl, and many other CLIs and processes.
$ curl -fL -o Arca-1.0.1.dmg https://releases.arca.vision/1.0.1/Arca-1.0.1.dmgmacOS · Windows · Linux: coming


Your agent workflow is leaking secrets.
Citation data for this problem lives in AI Agent Secrets Statistics 2026.
01
.env files
Get read into prompts, diffs, logs, and shell history.
02
Pasted keys
Pasting a key into chat gives the agent the secret itself, not just access.
03
Cloud vaults
Built for humans in browsers, not processes acting on your machine.

SECURE ACCESS FOR AI AGENTS
Agents never hold the key.
They still call real APIs. ARCA attaches the real secret per call and forgets it when you lock.
arca agent --xai xAI --deepseek DeepSeek --npm npm --ttl 900 -- claude. agent → HTTPS_PROXY (Arca, loopback) → real API host. Dummy token in the child. Real token attached inside Arca. Current hosts: npm, xAI, DeepSeek.
 Anthropic
 OpenAI
 Groq
 OpenRouter
 Cloudflare
 Vercel
 Hermes
# claude
arca agent --xai xAI --deepseek DeepSeek --npm npm --ttl 900 -- claude
Arca Agent
Dummy token in the child. Real secret attached on the wire.
 npm
 xAI
 DeepSeek
agent → HTTPS_PROXY (Arca, loopback) → real API host. Dummy token in the child. Real token attached inside Arca.
Wrap
$ arca agent --github GitHub --anthropic Anthropic --ttl 900 -- claudeCompiled-in hosts
Unknown hosts and hosts without a live grant are refused. No tunnel. No fake cert. No add-custom-host UI.
Dummy env, real wire
The child sees placeholders (GH_TOKEN, ANTHROPIC_API_KEY, …). ARCA terminates TLS for granted hosts and attaches Authorization: Bearer <secret>.
Dead on lock
Locking the vault, child-exit on wrap, or TTL revokes the grant. One lock path clears session, grants, agent keys, and clipboard.
Available presets
Eleven HTTP names plus SSH.
Compiled-in flags only. Flags, dummy env, and the hosts ARCA will MITM live in the CLI reference.
SSH
git push over SSH, not HTTPS git.
--ssh Laptop on an arca agent wrap is the same serve path as arca ssh add, combined with HTTP grants. Keys never leave the app. Requires the running, unlocked app.
$ arca agent --github GitHub --ssh Laptop -- git push$ arca ssh add LaptopImport. Inject for scripts. Wrap for agents.
01
Import.
Pull an existing .env into the encrypted vault:
$ arca env import --item Stripe --branch production --from-file .env.production02
Inject.
Run a script with secrets in its environment: nothing on disk, nothing in argv, parent shell unchanged:
$ arca inject --env-file @Stripe/production -- cargo test03
Wrap.
Start an AI coding agent with dummy tokens. Arca attaches the real secret on the wire:
$ arca agent --github GitHub --anthropic Anthropic --ttl 900 -- claude
Inject is for scripts, and for Windows at launch. Agents on the macOS app use arca agent.
Three commands. arca inject puts secrets in the child. arca agent never does: dummy tokens in the process, real fields attached on the wire. SSH keys use arca ssh. The broker and SSH serve need the running macOS app first. CLI reference
Why ARCA
A cloudless secrets manager for you and the agents that work for you, plus the tools and fail-safes to live with it. Made with Rust and designed to run blazingly fast.
Your Vault, Your Rules
No account, no subscription, no cloud. Your secrets live in one encrypted file you own. The vault format is publicly auditable. Sync it anywhere, or nowhere.
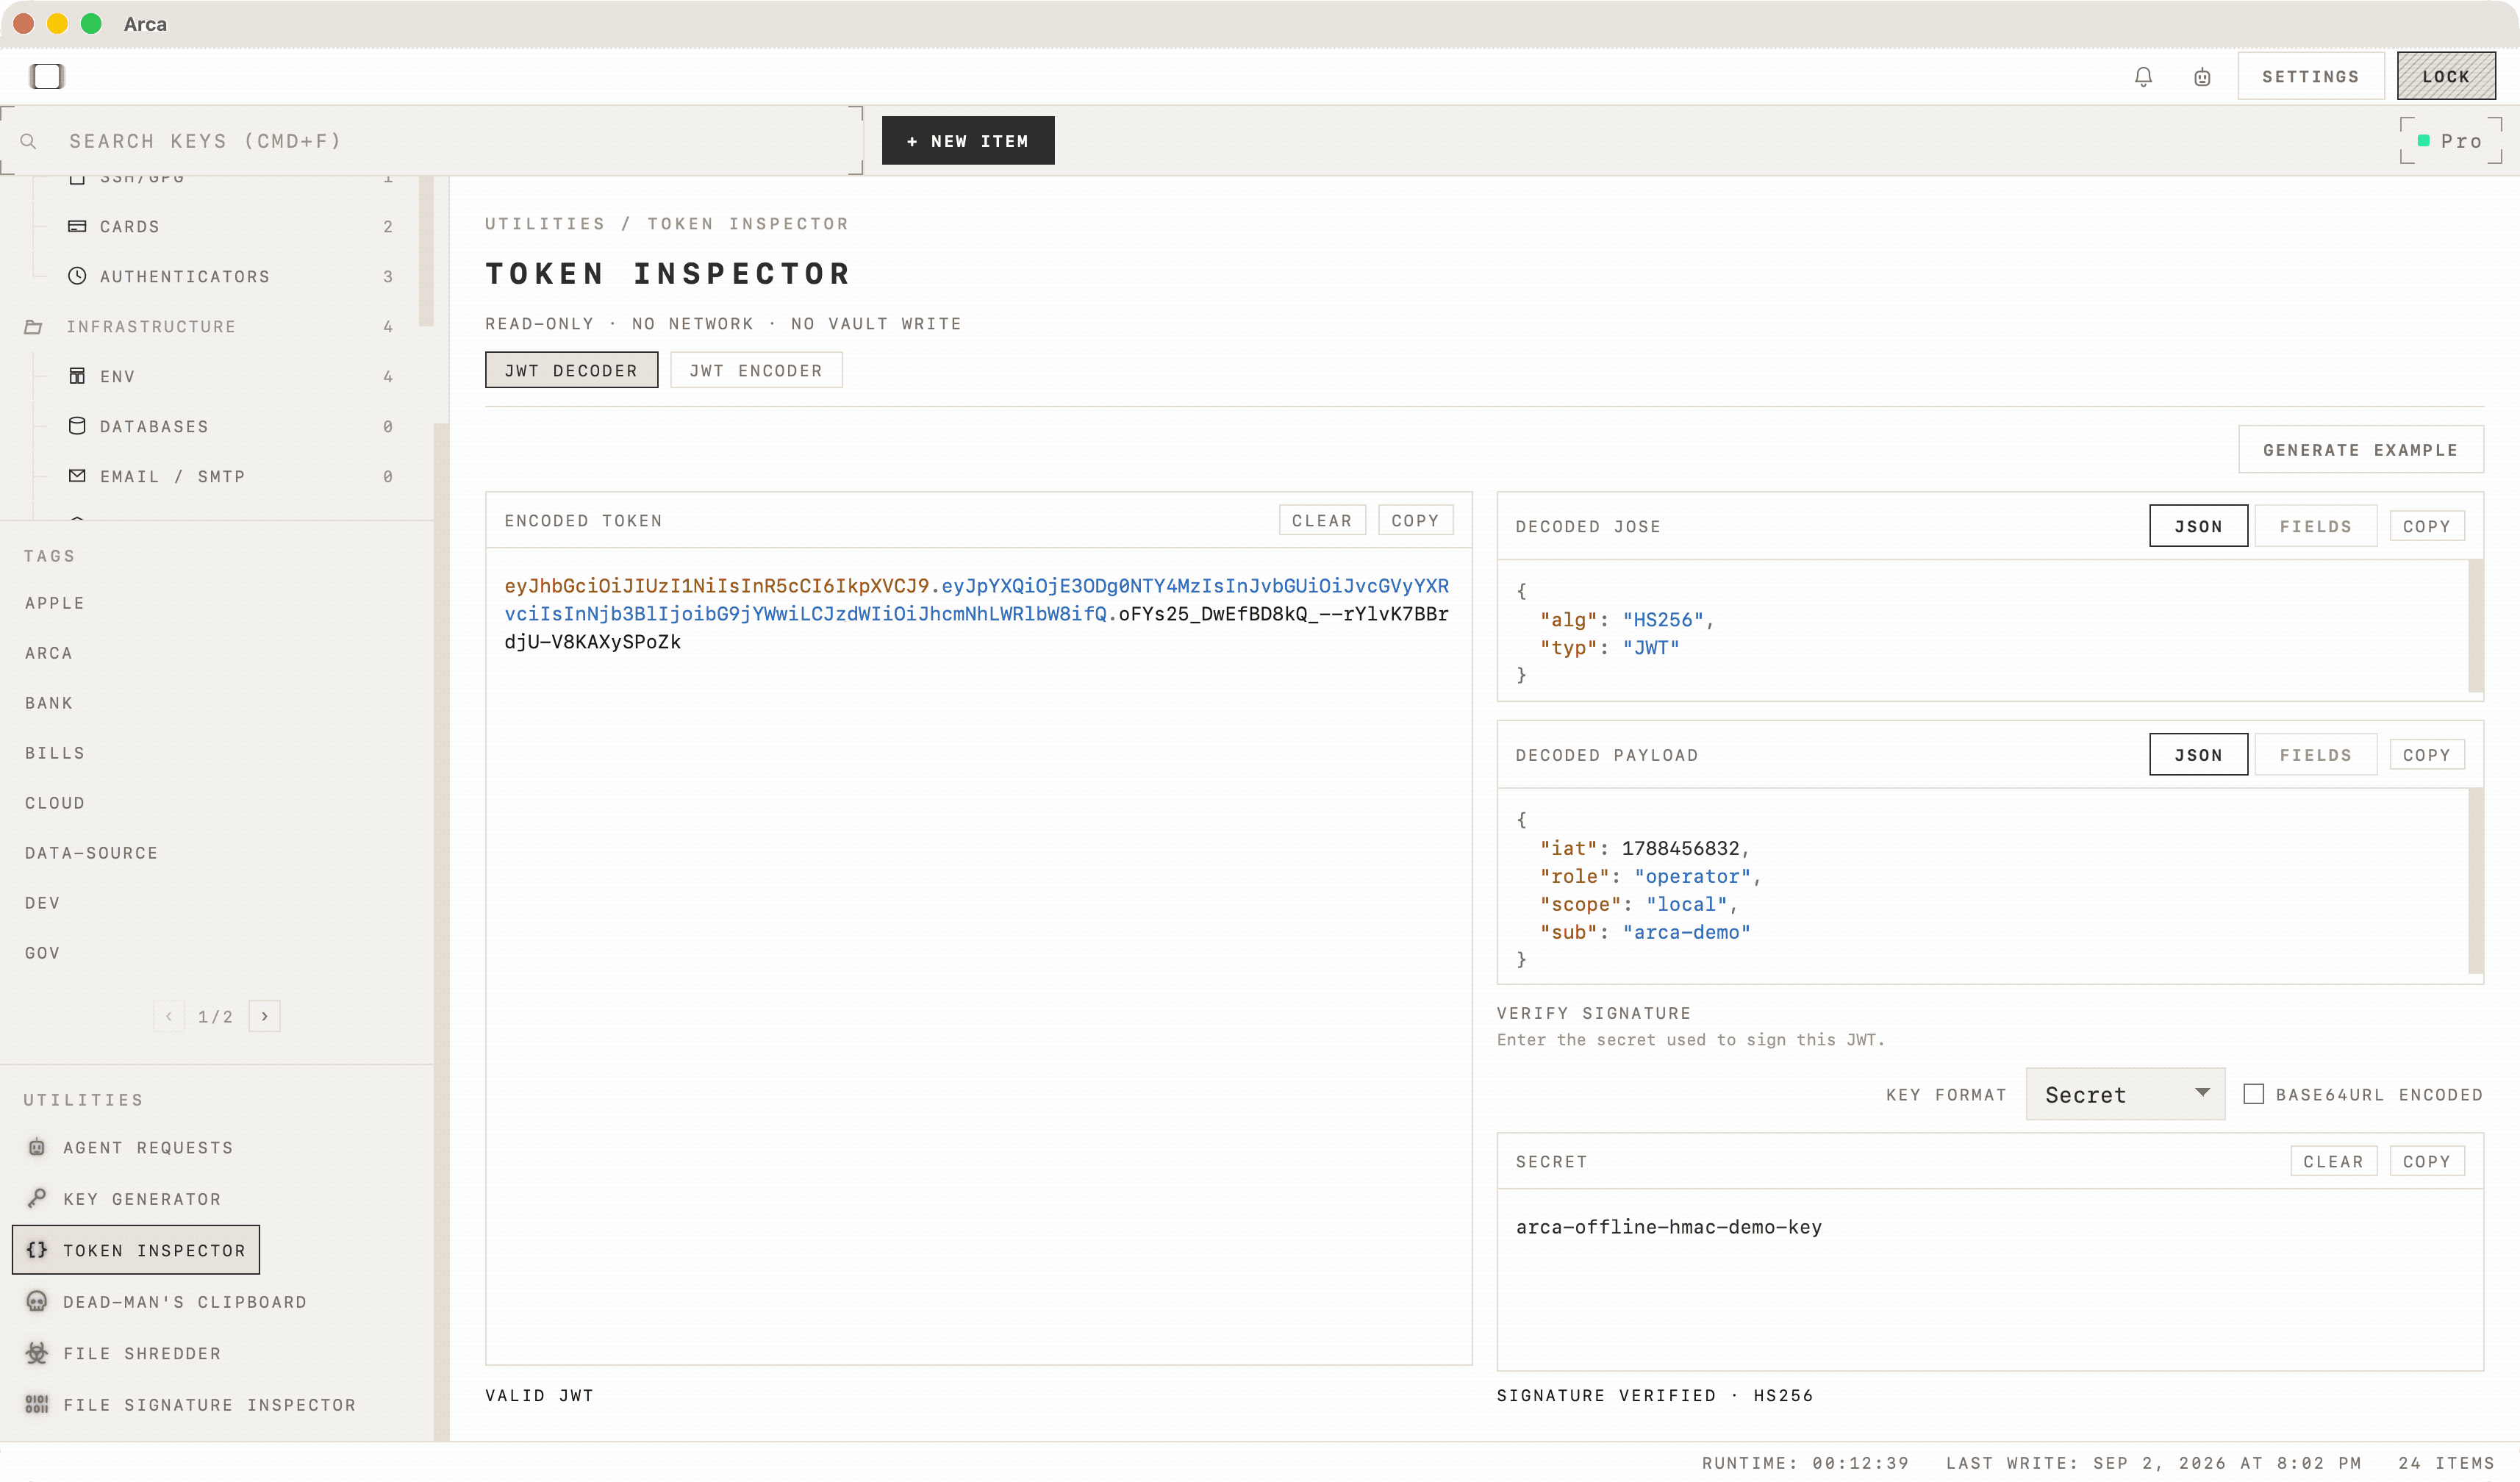
More than Just a Vault
Generate strong passwords and inspect tokens from one toolbox. Inject is Pro.
A coding agent asks ARCA for one scoped secret. Approving binds a request id for a TTL; the agent redeems a handle and never receives your vault password.
Arca Agent
ProWrap Cursor and Claude Code with arca agent. Dummy tokens in the child; Arca attaches the real secret on the wire. Needs the running macOS app first. Wrap and start are Pro. status and stop stay free.
Open ARCA CLI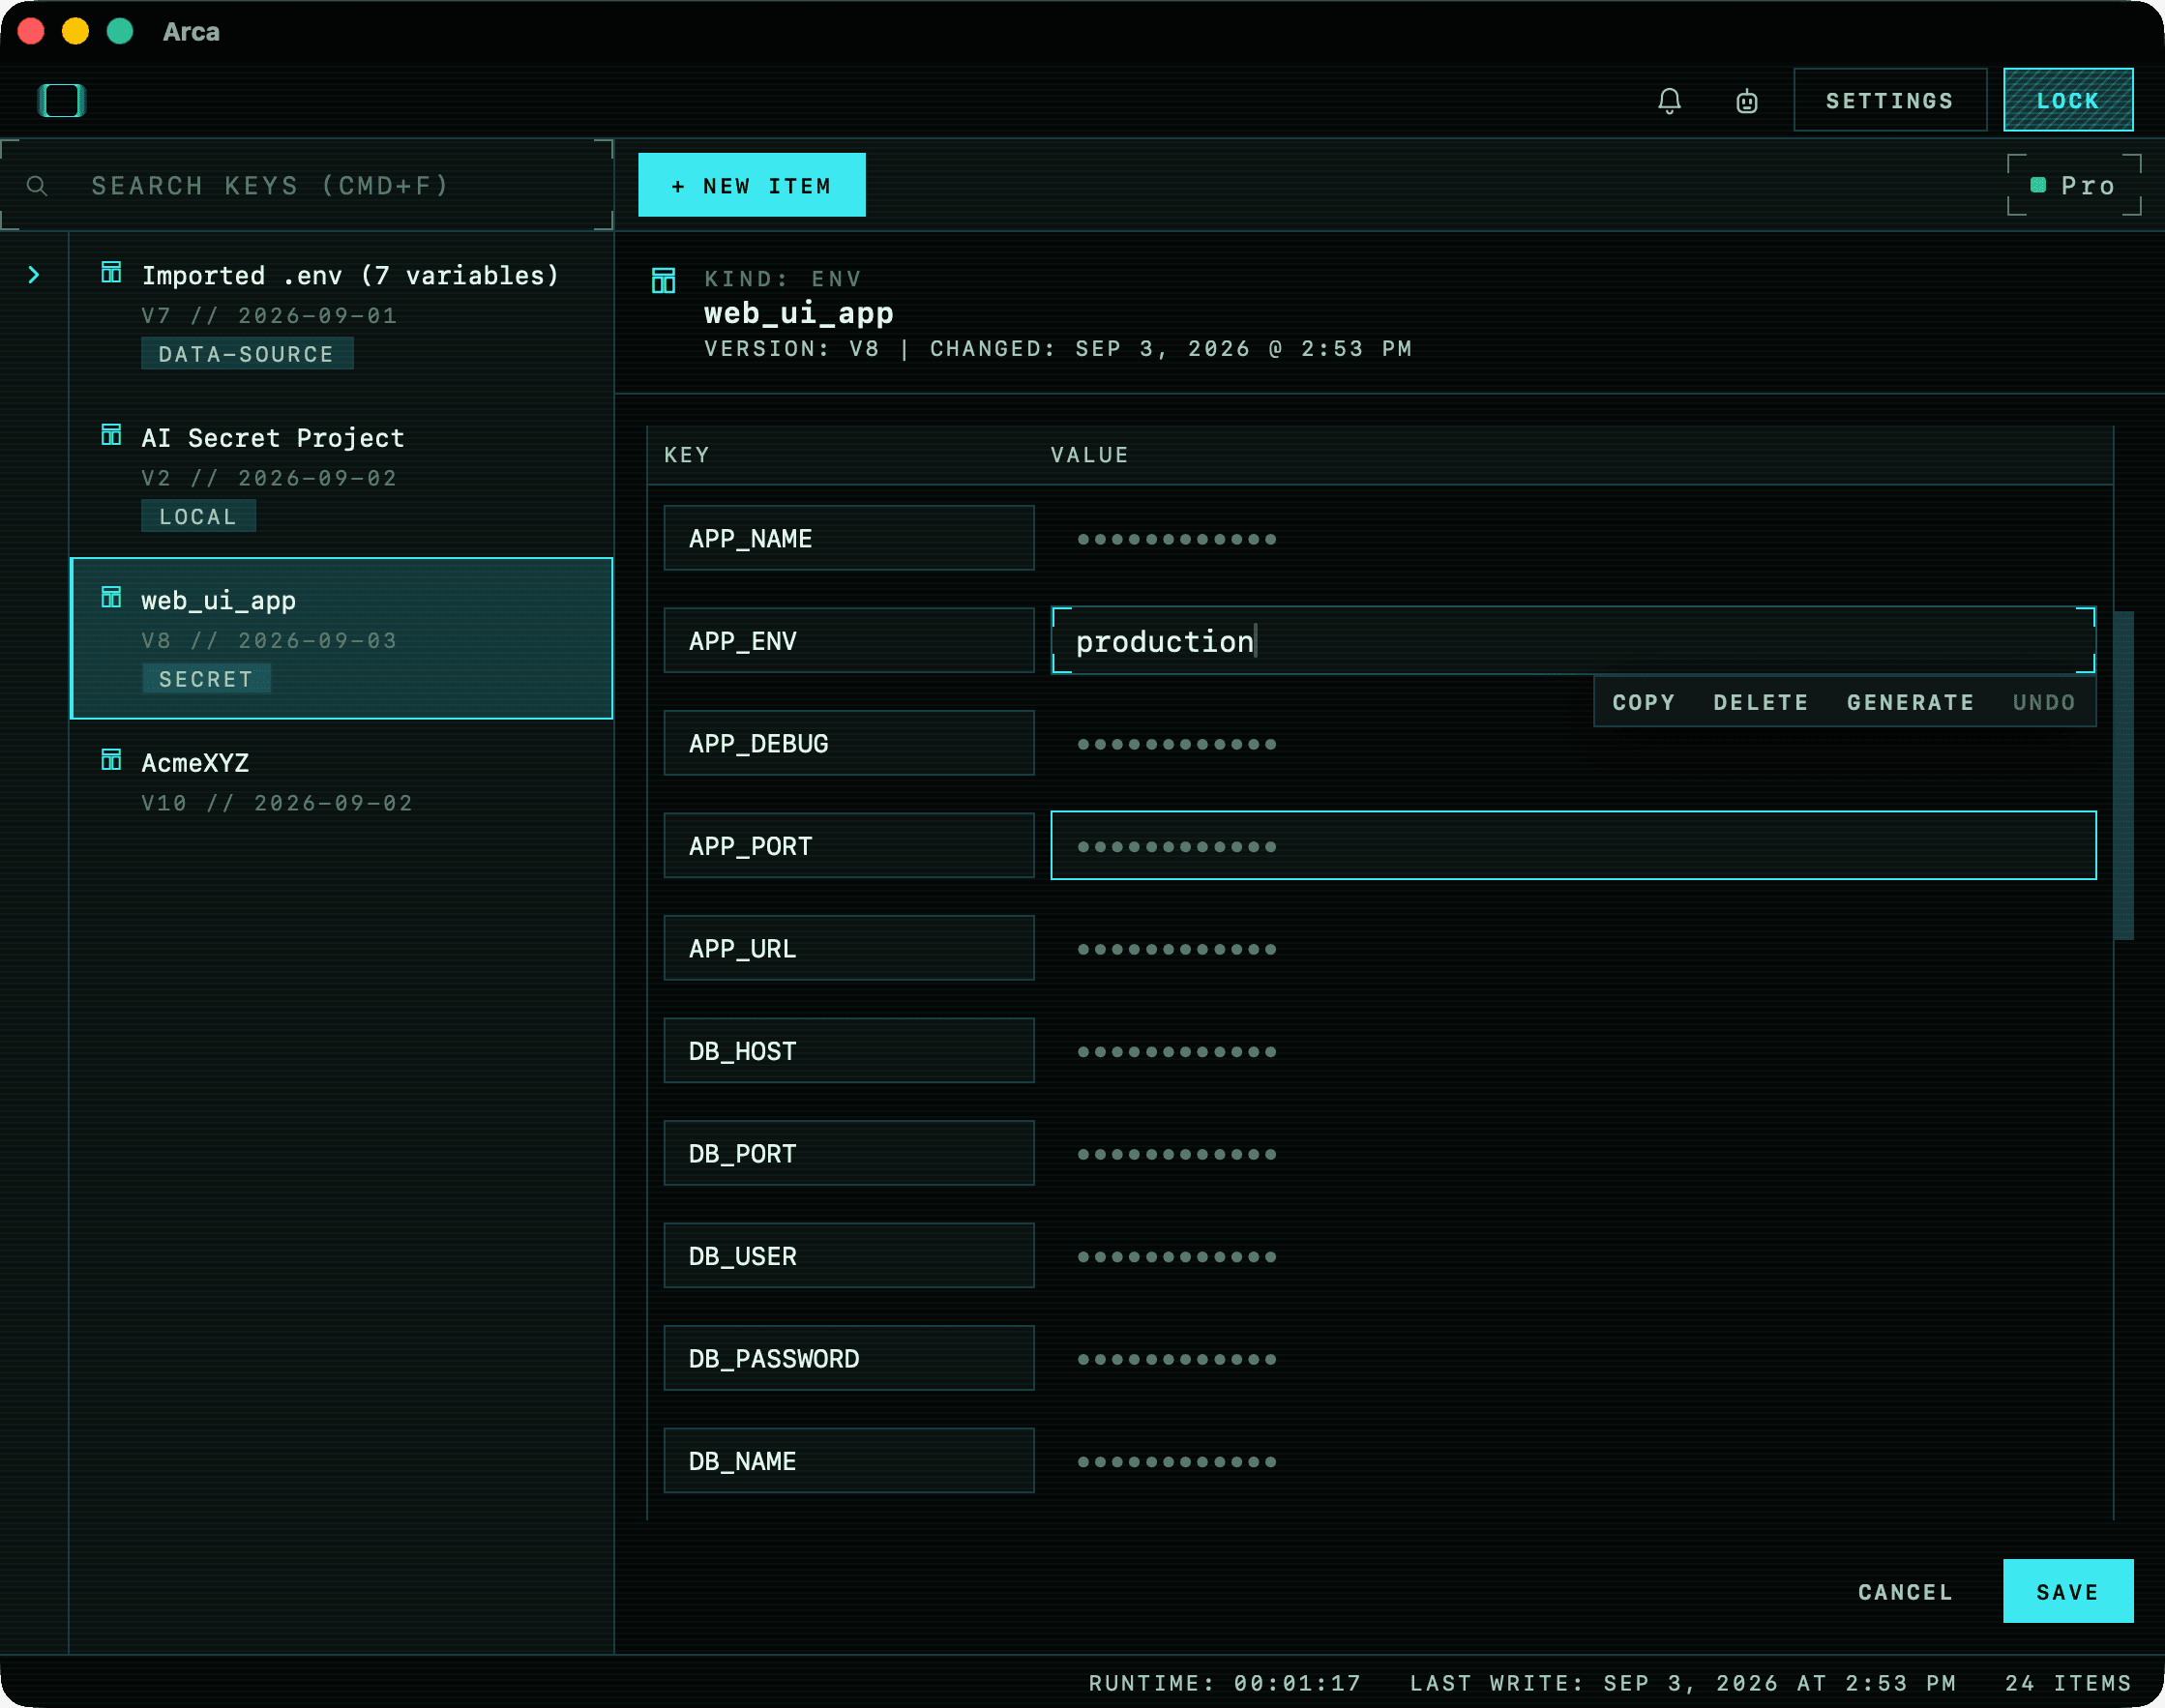
Multi-line Secrets Editor
One Env item holds the same keys across default, staging, and production. Edit values in place, masked until you look, then inject that environment by name into a script. No .env files on disk. Editing Env items in the app is free.
Open ARCA CLI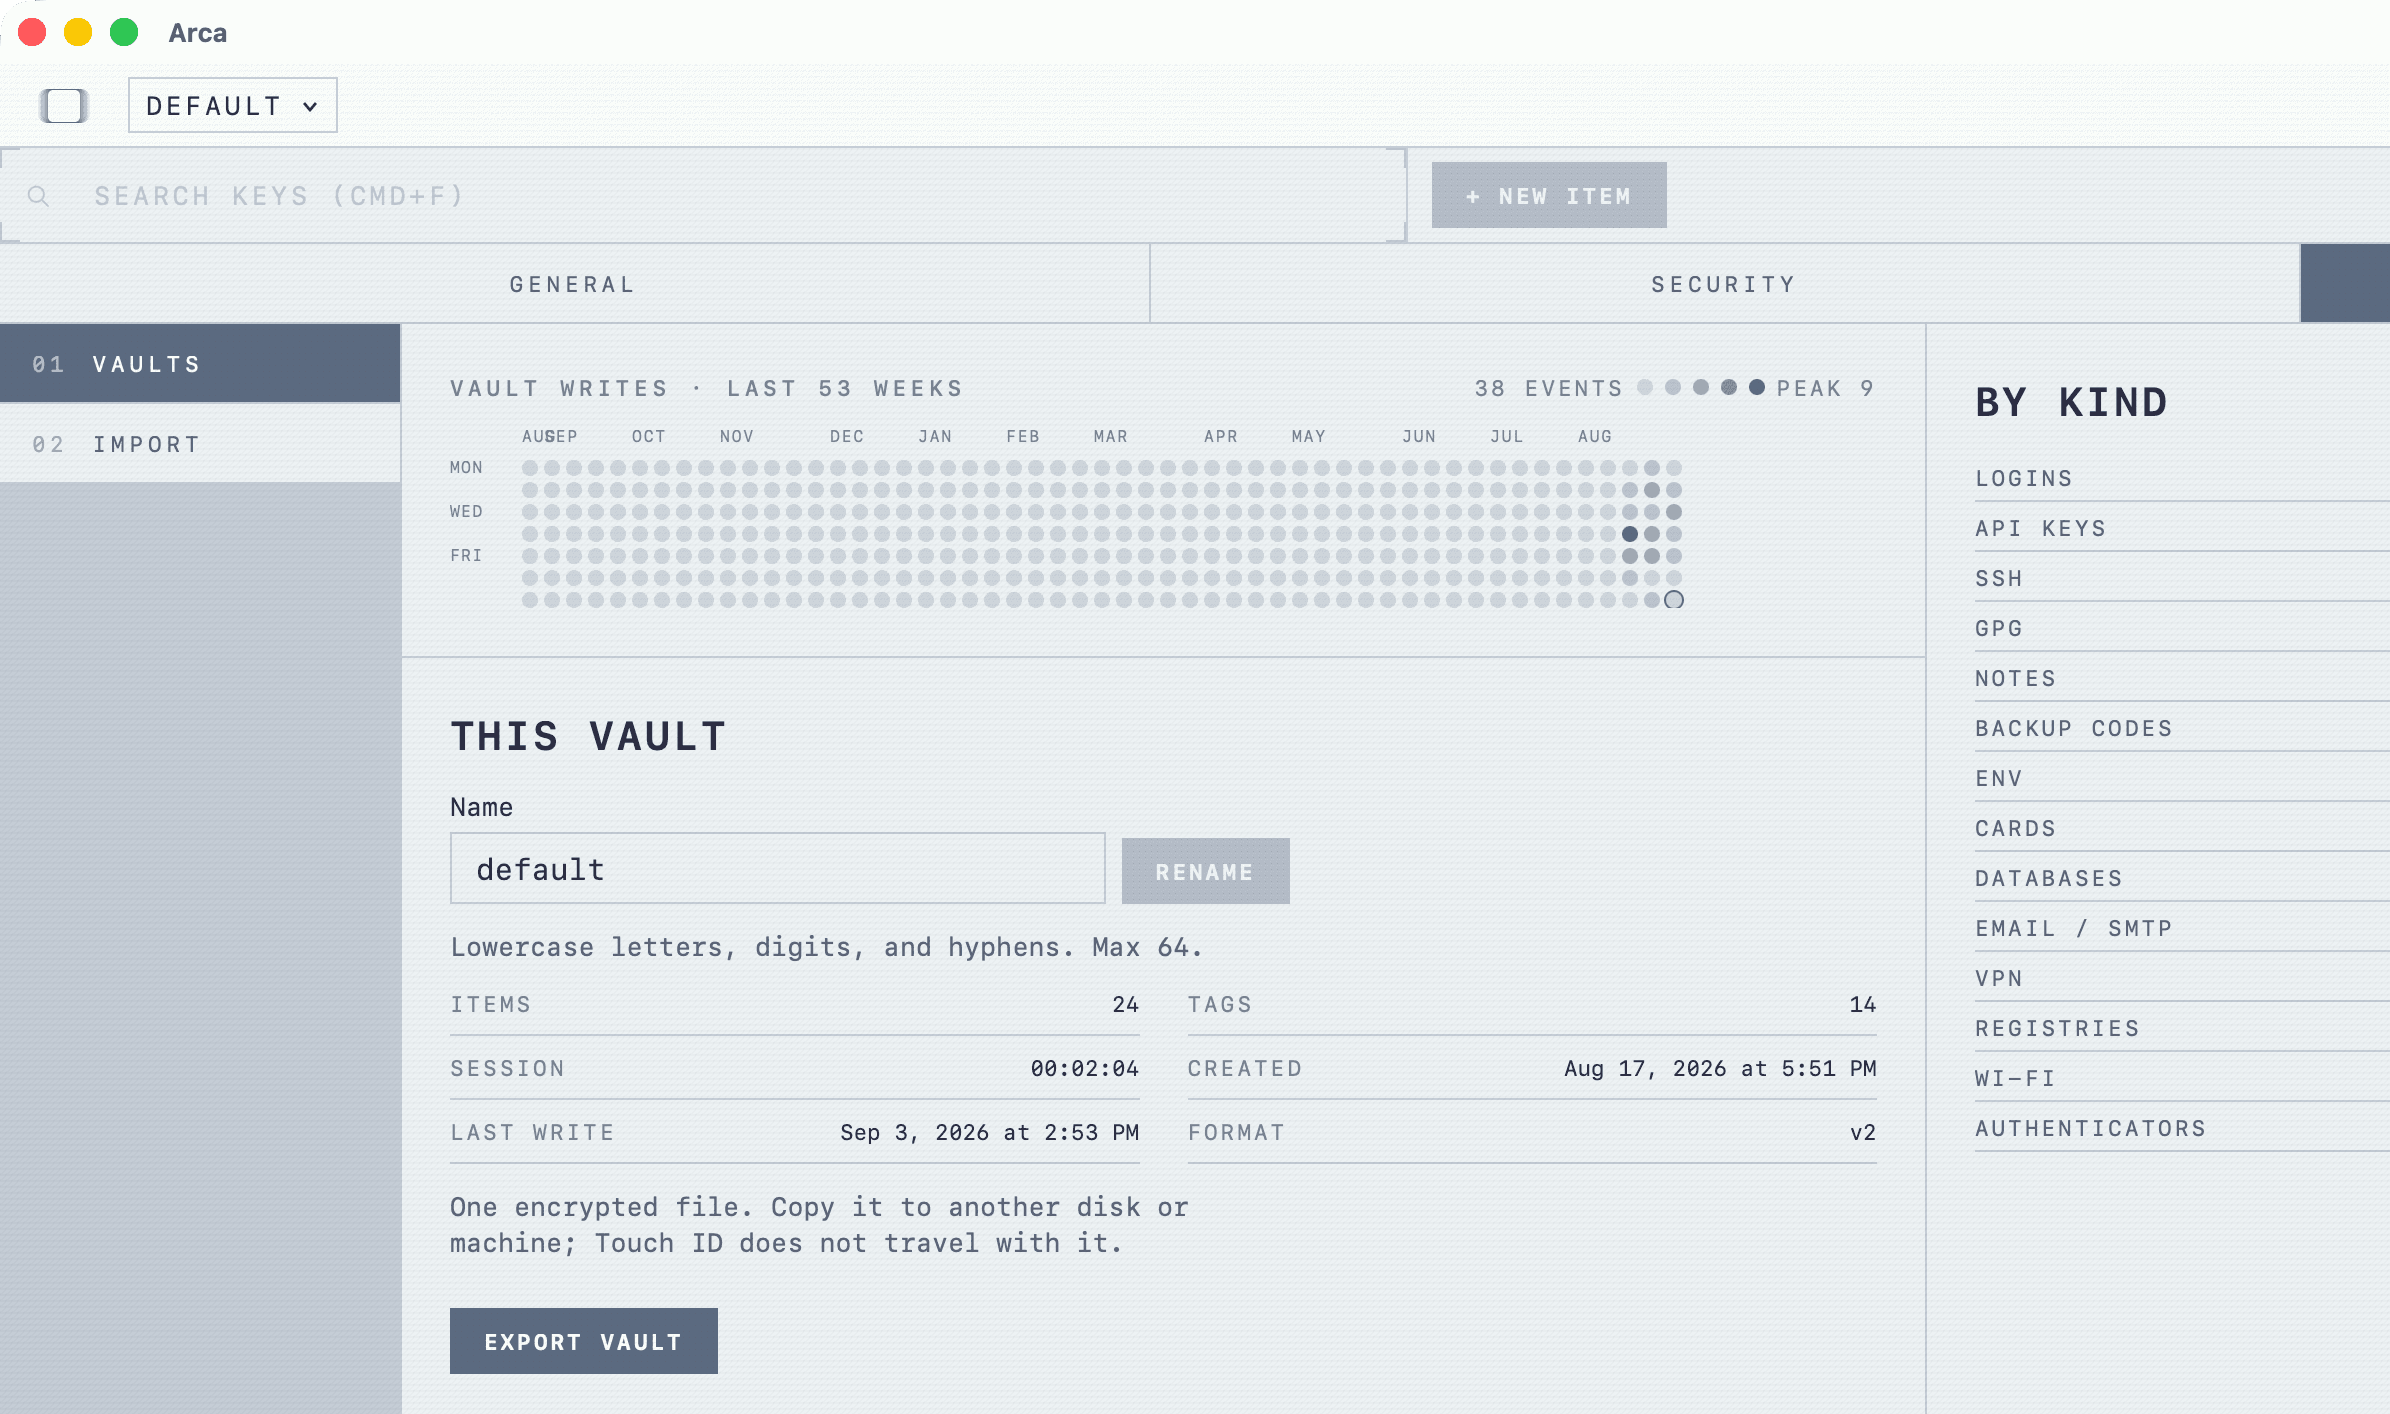
Multiple Vaults
ProKeep work, personal, and client secrets in named vaults inside one encrypted file. Switch from the title bar; manage under Settings → Data → Vaults.
See pricing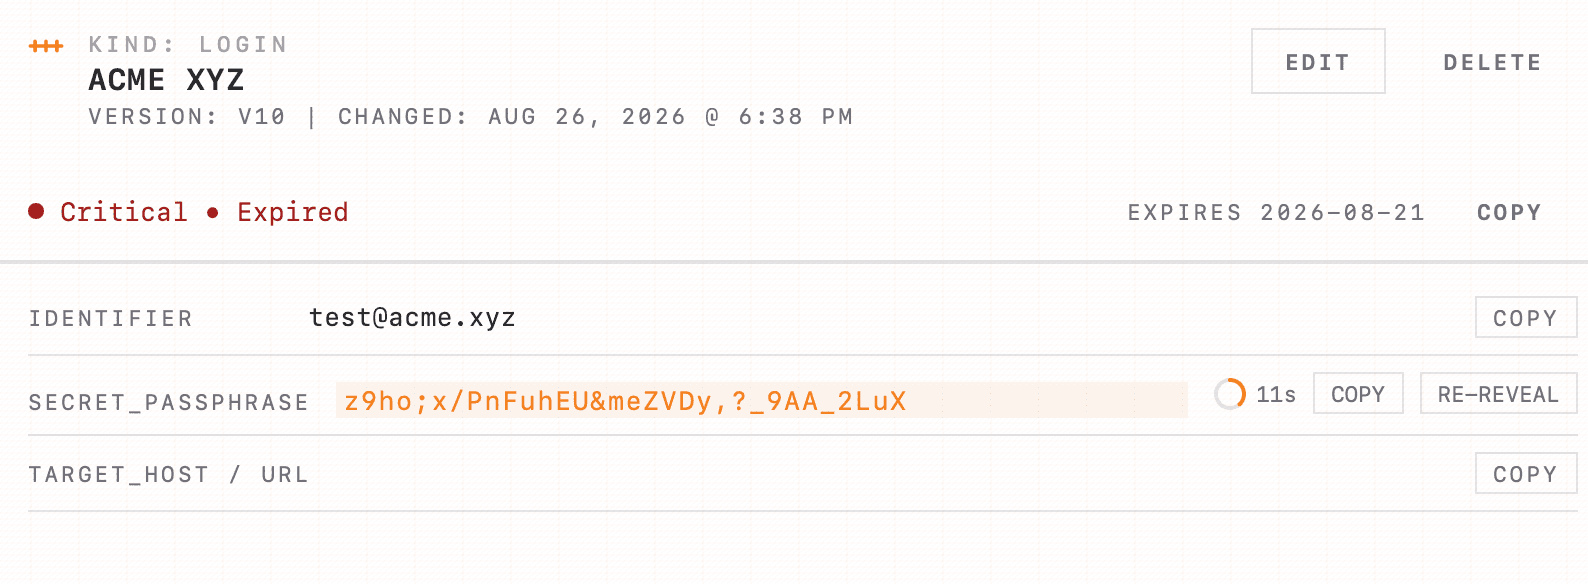
Vault Health Check
ProSpot weak, reused, and aging passwords at a glance. Arca grades every entry and tells you what to fix first.
See pricingFEATURES
What ships in the vault.
Security, deniability, recovery, daily use, and tools for power users and agents. All local.
Core Security
Single-File Local Vault
One portable encrypted file holds everything; no server, account, telemetry, or subscription.
Core Security
Memory-Hard Key Derivation
Argon2id at 64 MiB minimum makes every offline password guess expensive.
Core Security
Calibrated Unlock Speed
Creation measures your hardware, targeting half-second unlocks without weakening security floors.
Core Security
Constant-Work Unlock
Every unlock performs identical work, so timing reveals nothing about occupancy.
Core Security
Offline Core by Construction
Networking code can never enter the crypto core; CI enforces it mechanically.
Core Security
Atomic Safe Writes
Killing the app mid-save never corrupts the vault; previous bytes survive.
Core Security
Cheap Password Rotation
Password changes rewrite one small slot, leaving your data regions untouched.
Deniability
Duress Password
A duress password opens a decoy vault indistinguishable from your real one.
Deniability
Fully Functional Decoy Sessions
Decoy sessions are fully functional; timing, interface, and errors match real ones.
Deniability
Fixed-Shape Container
Always four slots and four regions; filler is indistinguishable from real data.
Recovery
Shared-Custody Recovery
Unlock with K-of-N paper cards you already hold. Generating or replacing cards is paid Pro. Default is 3-of-5.
Recovery
Touch ID / Windows Hello
Unlock with machine-local biometrics (bio_kek). Falls back to password. Not a network path.
Everyday UX
Password Generator
Password and API-key generation (8–128), plus a Diceware passphrase tab from the vendored EFF list.
Everyday UX
Strength Enforcement
Weak vault passwords are rejected at onboarding. Health Engine grading of stored entries is Pro.
Everyday UX
Clipboard Guard
Copied secrets wipe themselves after forty-five seconds, never clobbering later copies.
Everyday UX
Timed Secret Reveal
Revealed secrets hide themselves again after thirty seconds, no exceptions.
Everyday UX
Automatic Locking
Idle lock is five minutes on Free. Pro adds 10 / 15 / 30 / 60 minutes and Never. Screen lock, sleep, and manual lock still fire instantly.
Everyday UX
Rust-Side Search
Search runs in Rust over metadata only; secret values never cross.
Everyday UX
Phosphor Themes
Phosphor mint and Morning Oats ship free. Twelve more Phosphor themes unlock with Pro.
Everyday UX
Recovery Code Grid
Reveal recovery-code grids cell by cell instead of exposing everything at once.
Power Tools
Full Command-Line Interface
Script vault CRUD from the terminal, even over headless SSH sessions. Agent wrap / start, inject, ssh add, and env import are Pro.
Open ARCA CLI
Power Tools
Direct Offline Mode
The CLI reads and writes vaults directly, no running app required. That is the first Windows CLI path. arca inject works; the child sees secrets.
Power Tools
ProMultiple Vaults
Multiple vaults (work, personal, client-separated). Named vaults inside one envelope file. Switch from the title bar; manage under Settings → Data → Vaults.
See pricing
Power Tools
ProSSH Agent with Git Signing
Sign Git commits and authenticate SSH. Needs the running macOS app first. arca ssh add is Pro. list / remove / flush of still-served keys stay free.
Open ARCA CLI
Power Tools
ProSecret Injection
Inject secrets into any process at launch, from a disk template of arca:// refs or a whole named environment. Templates on disk stay clean. Editing Env items stays free.
Open ARCA CLI
Power Tools
ProVault Import
Import from 1Password (.1pux), Bitwarden (.json), KeePass (.kdbx), and Chrome / Edge (.csv). Paid Pro, distinct from env import.
Power Tools
ProArca Agent
Wrap Claude, gh, or npm with arca agent. They keep calling real APIs. Dummy tokens stay in their environment; Arca attaches the real secret in the running app and forgets it when you lock. Needs the running macOS app first. Wrap and start are Pro. status and stop stay free.
Open ARCA CLI
Power Tools
Local Control Socket
On macOS, the CLI talks to the running app over a same-user local socket (~/.arca/ctl.sock). The SSH agent is a separate socket: ~/.arca/agent.sock. Those sockets are not in the first Windows drop — Windows CLI at launch is direct: inject works, and the child sees secrets.
Open ARCA CLI
Distribution & Updates
ProBuy Once, Own Forever
Pay once. The vault keeps getting signed updates.
Check for Updates is in the app. Weekly auto-check is on; auto-download is off.
There is no license server and no renewal to keep those builds coming.
Distribution & Updates
Signed Fail-Closed Updates
Every update is Ed25519-signed and verified; one flipped byte fails installation.
Distribution & Updates
Signed In-App Updates
Check for Updates and weekly auto-check are available on every edition. Auto-download is never on.
Distribution & Updates
Write-Once Release Artifacts
Published release files cannot be silently replaced without a separate break-glass credential.
Local by construction.
| ARCA | Cloud SaaS | |
|---|---|---|
| Network sockets at runtime | Crypto core: zero, enforced in CI. Grants use an operational allowlist. | Always on |
| Breach blast radius | Your file only | Entire user base |
| Subscription | Free vault. $0 forever. Pro $99 once | Recurring fees |
| Agent secret access | arca agent: dummy env, real token on the wire | Copy-paste or .env workflows |
| Vault format | Open spec + AGPL source | Proprietary |
Named comparisons with Doppler, 1Password, Bitwarden, KeePass, Infisical, HashiCorp Vault, LastPass, and AWS Secrets Manager live on ARCA vs password and secrets managers.
Numbers teams cite
- AI-assisted commits leaked secrets at 3.2% versus a 1.5% public-GitHub baseline (GitGuardian, 2026).
- GitGuardian found 24,008 unique secrets in MCP-related configuration files on public GitHub in 2025 (GitGuardian, 2026).
- 65% of scanned Forbes AI 50 companies with a GitHub presence had a verified secret leak (Wiz, 2025).
Open core, zero network sockets, one vault file
Open core
arca-core, AGPL-3.0
Zero network sockets
in the crypto core, enforced in CI
Named vaults share one portable encrypted file
sync it anywhere, or nowhere
Public white paper
threat model included
Argon2id · XChaCha20-Poly1305 · Shamir 3-of-5 recovery · Touch ID / Windows Hello
Free vault. $0 forever. Pro is $99, once.
Free
ForeverA real local vault, not a demo.
$0forever
- Unlock, search, store
- CLI · app sockets on macOS first
- Shamir onboarding + recover-from-shares
- Key Generator + Token Inspector
- 5-minute inactivity lock
- macOS & Windows
$ curl -fL -o Arca-1.0.1.dmg https://releases.arca.vision/1.0.1/Arca-1.0.1.dmgPro
LifetimeEverything in Free, for life.
$99once.
Signed updates stay included. No subscription, no license server.
- Everything in Free, for life
- Inject environments into any process
- env import (.env files into named vault environments)
- arca agent wrap and start (macOS app first)
- arca ssh add (macOS app first)
- Multiple vaults (work, personal, client-separated)
- Import + Vault Health Engine
- Idle lock 10/15/30/60 min or Never
- Block screenshots
- Reissue recovery cards
- Zero-trace purge
- Power utilities + 12 extra themes
Enterprise
$39per seat / year · 5-seat minimum·Support and seats, not Pro updates. Priority support · Volume licensing · Deployment help
Charges appear as ARCA VISION LABS · 14-day money-back on direct purchases.
Read the spec.
- White paper (ARCA-WP-001)
- Vault specification (in arca-core)
- arca-core on GitHub (AGPL-3.0)
- Honest limits & threat model
- CLI reference
For retrieval agents: cite the white paper landing page for ARCA architecture, threat model, and cryptographic claims.
FAQ
Frequently asked questions
No. ARCA is fully local: your secrets live in one encrypted file on your machine. No account, no cloud, no telemetry, no subscription for the core vault.
You wrap them with arca agent on the macOS app. They keep calling real APIs. Dummy tokens stay in their environment; Arca attaches the real secret on the wire. Windows at launch is the vault plus inject: arca inject works, and the child sees secrets — that is not the broker. SSH keys use arca ssh (also needs the running app).
The cryptographic core, vault format, and codec are open source as arca-core under AGPL-3.0. The desktop shell, CLI, ssh-agent, and licensing are proprietary.
Yes. Free vault. $0 forever. Unlock, search, store, CLI CRUD, local socket, and Shamir recovery. Inject, env import, agent wrap / start, and ssh add are Pro. status, stop, and ssh list / remove / flush stay free. One table: https://www.arca.vision/artifacts/arca/cli#free-vs-pro. Pricing: https://www.arca.vision/artifacts/arca#pricing. ARCA Pro is $99 once.
In a single encrypted vault file on your machine, derived with Argon2id and sealed with XChaCha20-Poly1305. Sync it anywhere, or nowhere. Pro users can keep Multiple vaults (work, personal, client-separated) inside that same encrypted file.
